A complete, queryable view of your IT/OT and cybersecurity assets in 30 days. We set up CAASM with you, then hand-craft a report on what we found: your coverage gaps, your policy deviations, and what to do about them. No cost, no obligation, no lock-in.
Receive a detailed presentation and comprehensive report on findings
Get our expert remediation recommendations
No obligation to continue, no subscription, no lock-in. Keep your data and report even if you decide not to move forward.
Outcomes
Comprehensive Asset Inventory: A complete overview of all your IT and OT assets
What’s Good: Highlight strengths and well-managed areas
What’s Bad: Vulnerabilities and risks
Gaps: Uncovering blind spots in your current asset management approach
Expert Recommendations: Actionable steps for remediation and improvement
Presentation: A walkthrough of the findings and recommendations by our cybersecurity experts
What SJULTRA customers say
We acquired several new businesses and needed to quickly discover what was out there across multiple new OT networks -- there was no other way to solve this problem.
CIO
Energy Company
Our Red Team security audit discovered that some assets were not being patched. Using this service we found out a lot more unknown unknowns that need to be fixed to avoid security breaches.
CSO
Global Finance
We didn't have the team, time, or the tools to observe our cybersecurity and it was a board-level risk. That's now solved with this service.
Head of IT
Education
Frequently Asked Questions
Can I self-serve?
You can go direct to SJULTRA CAASM and learn from scratch, or you can get their faster and leverage our experience.
What’s the catch?
No catch. No cost. No obligation.
How long does it take?
We kick off within a week of hearing from you.
Any limitations?
We limit the amount of integrations and assets in the trial.
8 Compelling Events that drive CAASM projects
Complex IT/OT
Our CMDB was inaccurate and out of date, because our IT/OT changes all the time and our tools are like silos of data. There’s no single source of truth we can trust.
skills and tools
Our team turnover has left us with missing skills and less bandwidth, so these important cybersecurity jobs aren’t getting done.
Red Team Audit
The Red Team found unpatched devices, and this solution found out why: they weren’t being patch managed.
M&A
We bought several companies and there was no way to “see” across them all, which is what we needed to merge them.
MSP Offboarding
Prepare for MSP people and process handover by using CAASM to analyze all systems and their integrations, answering important queries.
Technology Migration
Migrating on/off the cloud or off-boarding VMware are common compelling events where CAASM provides full sight.
New Leadership
As a new CIO, my 90-day plan includes surveying the IT landscape: and if I can’t do that, then there’s an immediate problem.
Compliance Failure
We can’t prove to the auditor that we are following our own security policies. This solution codifies our policy into practice.
Outcomes from the SJULTRA CAASM Solution
Features
Automated inventory and discovery of assets
Continuous monitoring and reporting of asset data
1,000 security and IT management integrations
Customizable dashboards and reports
Remediation workflow automation
Policy enforcement and compliance monitoring
User behavior and risk analysis
Benefits
Enhanced cybersecurity posture
Increased operational efficiency
Reduced risk and exposure to threats
Compliance with industry and regulatory standards
Cost savings through automation and streamlining of processes
Streamlined communication between IT and security teams
Quick and easy deployment
Top 3 objections to starting a CAASM project
We have Existing cybersecurity tools
Who needs more tools? Our SJULTRA CAASM is different in that it aggregates *everything*, which can lead to removing other tools to save money. No other tool does what SJULTRA CAASM does.
CAASM isn't a priority Right Now
Cybersecurity asset management isn’t exciting…until it is. Security breaches, failed audits, and wasted spend is the kind of excitement you can do without.
We don't have this problem at all
CMDB uptodate and accurate? Got multiple MDRs? XDRs? Patch Management? Vulnerability Analysis? Do they all tally and say the same thing — or do you have unknown unknowns?
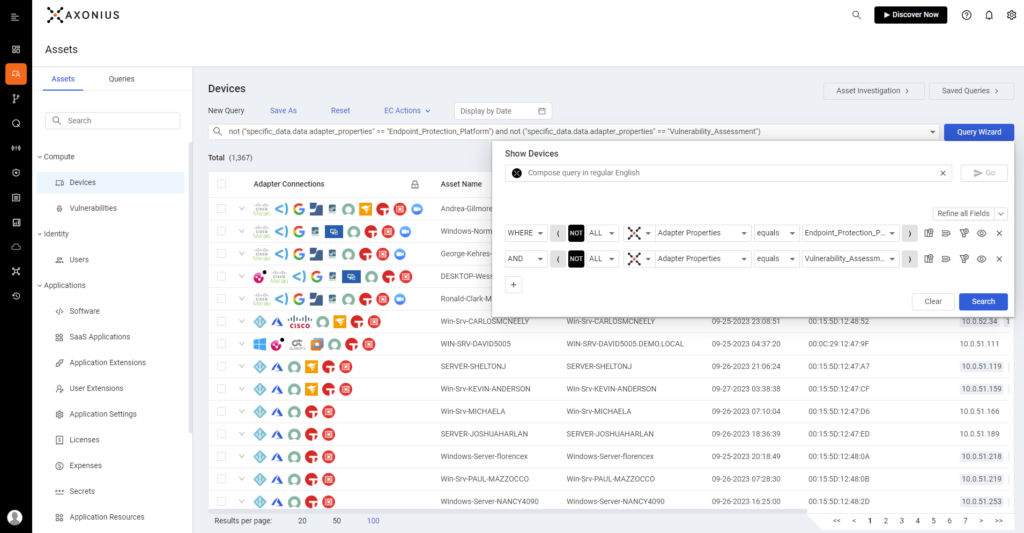
Detailed view of individual devices, including aggregated data from multiple sources
Query wizard for creating complex searches (e.g., Windows devices without McAfee, public cloud assets not scanned for vulnerabilities)
User permission and configuration queries
Cloud asset compliance add-on (e.g., CIS benchmarks for various cloud providers)
Automation of actions based on policy violations
Various response options: notifications, ticket creation, scheduled scans, user management in Active Directory
Over 115 pre-built actions available
Any query can be turned into a dashboard chart for easy visualization and tracking over time
Watch an Axonius demo
Why CAASM?
Asset management in security is hard because the data lives in silos that disagree with each other. Your CMDB, your EDR, your vulnerability scanner and your cloud console each hold a partial truth.
That makes the basic questions expensive to answer: which devices are missing an agent, what is unmanaged, which cloud instances are misconfigured.
Axonius aggregates and correlates all of it into one system of record — you cannot prioritize what you cannot see.